GitLaw How-To guides
How to get a document signed
To get a document signed in GitLaw, open it, click Share, then eSign. GitLaw detects the contract parties from signature blocks placed in the GitLaw editor (or you add signers yourself), lets you review the recipients and place signature fields, then emails each signer a link to sign in their browser. Once everyone has signed, you receive a final, tamper-sealed PDF. E-signature is built in and free.
Before you start: a finalised document in GitLaw, and each signer's email address.
How do I send a document for signature in GitLaw?
GitLaw includes free built-in e-signatures, so you can send a finalised document for signing without leaving the platform or paying extra:
-
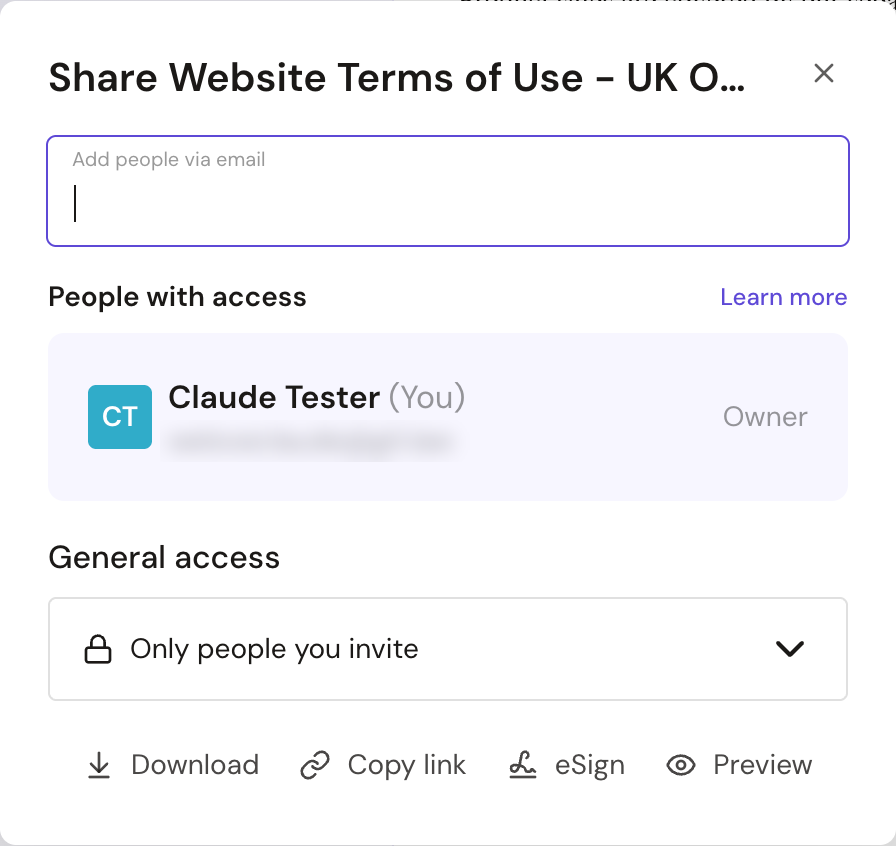
Start signing: open the document, click Share at the top right, then eSign at the bottom of the panel. You can also choose Start eSign from the … menu next to the document title. Or ask the Agent: "Send this for signature".
-
Add yourself if you sign too: GitLaw asks for your signature details. Click Add to sign the document yourself, or Skip.
-
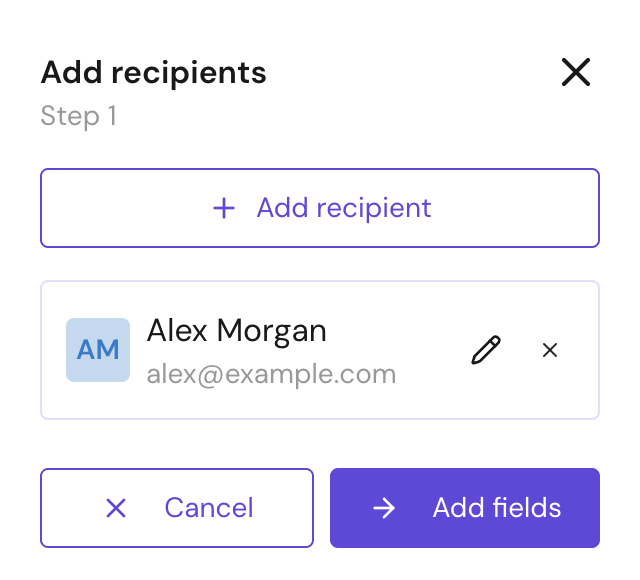
Add recipients: click Add recipient and enter each person's name, email and role (for example Needs to sign). If the document contains signature blocks placed in the GitLaw editor, GitLaw detects the parties for you. Click Add fields when everyone is listed.
-
Place signature fields: click Auto-place fields to let GitLaw place them, or open Place fields manually. You can move any field before sending.
-
Send: click Send. Each signer receives an email from
[email protected]containing the document name, their role, and a button to sign in their browser. No GitLaw account is required to sign.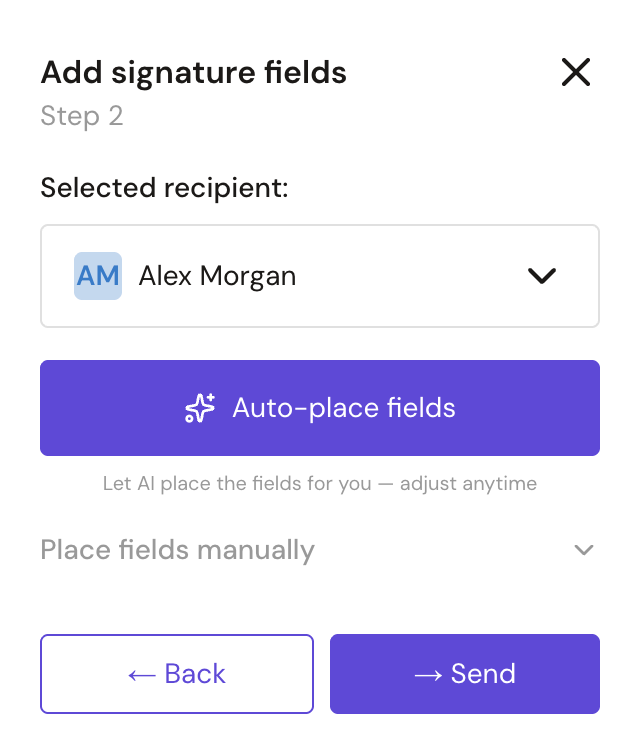
-
Track status: the document moves through three states: Draft → Awaiting Signatures → Fully Signed. You can see who has signed and who has not from the document view, and send a reminder to anyone outstanding using Send reminder.
-
Receive the signed PDF: once every party has signed, GitLaw generates a final, tamper-sealed PDF and attaches it to the document. All participants receive a copy by email. The document is then locked against further edits.
What is in the signing audit trail?
Every signing event produces a secure audit file stored alongside the signed PDF. It captures:
| Data point | Purpose |
|---|---|
| Timestamp of each signature | Legal audit trail |
| Signer IP address | Identity evidence |
| Device / browser fingerprint | Dispute resolution |
| Email address used | Authentication match |
| Full transaction log | Sent → Viewed → Signed → Completed |
This meets industry standards, equivalent to DocuSign or HelloSign audit certificates, and is legally enforceable under the ESIGN Act / UETA (US), Electronic Communications Act 2000 (UK) and eIDAS Regulation (EU).
Good to know before you send
- Collaboration history is excluded. The version sent for signature contains only the finalised document. Chat, comments and drafting history are not shared with signers.
- Free, always. E-signature is included in GitLaw at no extra cost and is not metered.
- Signing from the Agent. If you prefer, simply tell the Agent to send the document for signature. It will guide you through the same flow.
Frequently asked questions
Do signers need a GitLaw account?
No. Each signer receives an email from [email protected] with a button to sign in their browser. No GitLaw account is required to sign.
Is GitLaw e-signature legally binding?
Yes. Every signing event produces a secure audit file, and signatures are legally enforceable under the ESIGN Act / UETA (US), the Electronic Communications Act 2000 (UK) and the eIDAS Regulation (EU).
Does e-signature cost extra?
No. E-signature is included in GitLaw at no extra cost and is not metered.
Related articles
Reviewed by the GitLaw team. Last updated 4 November 2026.