
Adam Frankel
General Counsel · Technology & AI
15+ years as General Counsel to technology, cloud & AI companies
This document outlines the Acceptable Use Policies for GitHub, detailing restrictions on content and conduct related to user safety, intellectual property, privacy, and authenticity. It serves to ensure a collaborative and safe environment for all users by prohibiting unlawful, harmful, or disruptive activities on the platform.
1. Compliance with Laws and Regulations
3. Intellectual Property, Authenticity, and Private Information
4. Spam and Inauthentic Activity on GitHub
7. Information Usage Restrictions
Short version: We host a wide variety of collaborative projects from all over the world, and that collaboration only works when our users are able to work together in good faith. While using the Service, you must comply with our Acceptable Use Policies, which include some restrictions on content and conduct on GitHub related to user safety, intellectual property, privacy, authenticity, and other limitations. In short, be excellent to each other.
Capitalized terms used but not defined in these Acceptable Use Policies have the meanings assigned to them in your main agreement with us — the GitHub Terms of Service or GitHub Customer Agreement, or the GitHub Corporate Terms of Service or other legacy GitHub contract, or a Microsoft volume licensing agreement. For customers subject to the legacy Corporate Terms of Service, "you" and "your" refer to "Customer" or "Users". "We", "us", and "our" refer to "GitHub".
You are responsible for using the Service in compliance with all applicable laws, regulations, and all of our Acceptable Use Policies. These policies may be updated from time to time and are provided below.
We do not allow content or activity on GitHub that:
is unlawful or promotes unlawful activities;
is sexually obscene or relates to sexual exploitation or abuse, including of minors;
is libelous, defamatory, or fraudulent;
is discriminatory or abusive toward any individual or group;
is false, inaccurate, or intentionally deceptive information and likely to adversely affect the public interest (including health, safety, election integrity, and civic participation);
harasses or abuses another individual or group, including our employees, officers, and agents, or other users;
threatens or incites violence toward any individual or group, especially on the basis of who they are;
gratuitously depicts or glorifies violence, including violent images; or
is off-topic, or interacts with platform features in a way that significantly or repeatedly disrupts the experience of other users.
We do not allow content or activity on GitHub that:
infringes any proprietary right of any party, including patent, trademark, trade secret, copyright, right of publicity, or other right;
unlawfully shares unauthorized product licensing keys, software for generating unauthorized product licensing keys, or software for bypassing checks for product licensing keys, including extension of a free license beyond its trial period;
impersonates any person or entity, including any of our employees or representatives, including through false association with GitHub, or by fraudulently misrepresenting your identity or site's purpose; or
violates the privacy of any third party, such as by posting another person's personal information without consent.
This is a preview. The full template is free on GitLaw.
5.0 out of 5 on Google
Read reviewsAs seen in


This version is drafted for US law generally. Contract, employment and consumer rules vary by state — for example on non-competes and at-will employment. Tell GitLaw which state applies and it adjusts the draft.
A template isn't binding on its own - like any contract, it becomes binding once it's properly completed and signed. Templates in our curated library are professionally drafted for US or UK law; review any template before you sign it.
Yes. Chat with GitLaw to edit any section, or make changes directly in the editor.
Yes, read about team plans here.
Describe what you need in the chat and GitLaw will draft it for you.
Templates in our curated library are professionally drafted for US or UK law. The wider library comes from the GitLaw community and public sources - a solid starting point, but check any template fits your situation before you rely on it.
Mostly US and UK law. Some templates use general commercial terms that work across jurisdictions, and many note which law they're written for.
It depends on the situation. Templates work well for routine business agreements. For anything involving significant money, complex IP, employment, or areas you're unsure about, it's worth getting professional advice before you sign. GitLaw provides templates and tools, not legal advice.
Open any template in GitLaw and describe the change you want in the chat — 'make clause 4 mutual' or 'add a 30-day notice period', for example. GitLaw drafts the revised language and shows it as a suggested edit. You accept, reject, or keep editing from there.
Yes. Upload a Word, PDF, or Markdown file and GitLaw will open it in the editor. You can review, edit, or chat with GitLaw about it the same way you would with any template from the library.
Every template opens in an editor with an AI agent alongside it.
Pick a template and open it. Nothing to download, and no credit card to start.
Free to open
Describe your situation in chat and the agent adapts the wording, clause by clause.
Tracked changes you can review
Share it for negotiation, then collect signatures without leaving GitLaw.
eSign included
Trained on 5,500+ clauses and specialist areas of law. Built with a standards committee of independent lawyers.
Adam Frankel
General Counsel · Technology & AI
15+ years as General Counsel to technology, cloud & AI companies
Juliana Calil
Principal Counsel · Technology & Entertainment
20+ years in-house at Google, Intel, Disney and Looker
Adam Wardel
General Counsel, Data Privacy Officer & AI Advisor
12+ years leading legal & privacy for SaaS and AI companies
John Hoffman
Associate Director, Corporate Counsel · Life Sciences & Technology
20+ years in corporate counsel, incl. senior counsel at Certara
Richard Nohe
General Counsel · Telecom, Cloud & Data Centers
20+ years in-house, regional General Counsel at BT across 30+ countries
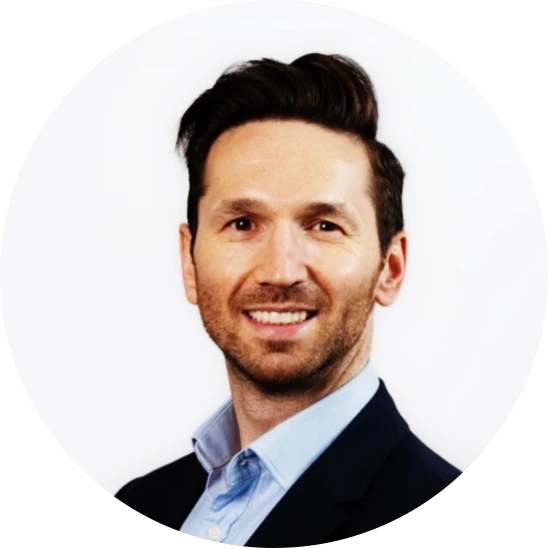
Joe Al-Khayat
General Counsel · Technology & High-Growth Companies
Cross-jurisdictional M&A and SaaS contracting across the UK, US & Australia
Joshua Woo
Technology, AI & Privacy Counsel · APAC
Former Goldman Sachs Executive Director for AI, cybersecurity & privacy in APAC
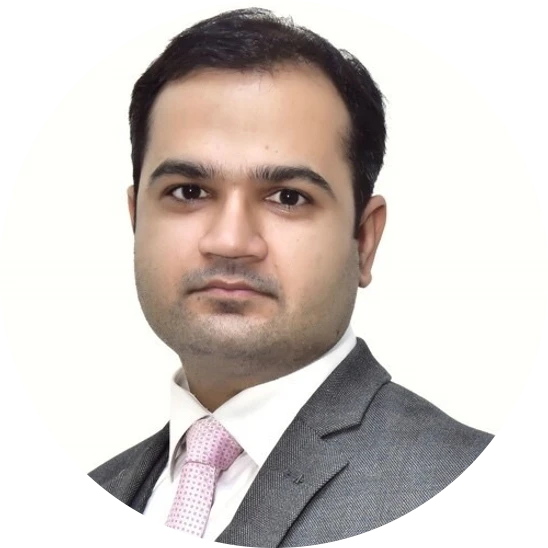
Sahil Verma
International Business & Investment Lawyer
13+ years in business law, investment law & dispute resolution
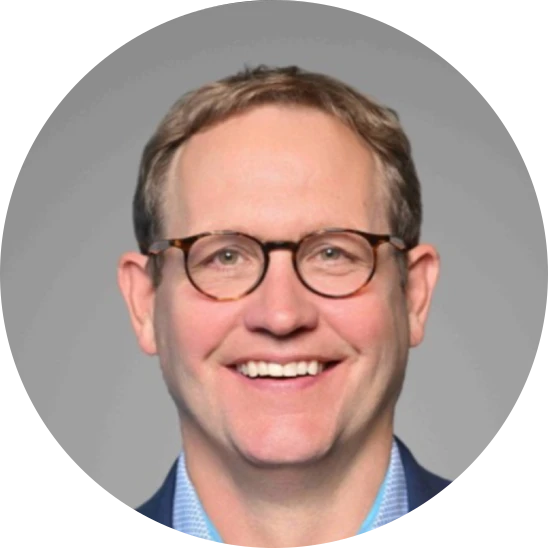
Matthew Willis
CRO & General Counsel · SaaS
Former President of the ACC's 2,200-attorney Chicago Chapter · JD + Kellogg MBA
Mayowa Ogunrinola
Legal Consultant · Fintech & AI Compliance
Regulatory strategy, AI governance & data protection for fintech and AI
Steven J. Shanker
Partner and Chair of Corporate and Employment Law
25+ years as a corporate & employment attorney in New York
As seen in
No sales calls, no credit card. Just chat with GitLaw.
GitLaw provides templates and tools, not legal advice. Templates are a starting point, not a substitute for advice on your situation - for anything significant, speak to a qualified lawyer.